How to Setup DNS
DNS Blog
Anycast DNS Explained: Faster and More Resilient Resolution
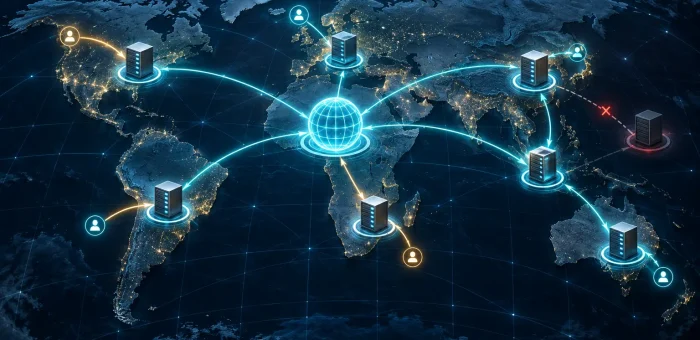
DNS has to answer users wherever they are, often before a website, application, or email service can do anything useful. If every query must travel to one distant server, network delay and a single infrastructure failure can affect the experience. Anycast DNS addresses this challenge by allowing multiple distributed servers to provide a service through the same IP address.
Routing systems direct each query toward an available location based on the network’s current path selection. The result can be lower latency, wider capacity, and better resilience than a service operating from only one location. The idea sounds simple, but a reliable deployment depends on coordinated routing, synchronized DNS data, health checks, and careful operations.
What is Anycast DNS?
In an Anycast design, DNS servers in multiple locations advertise the same service IP address. Internet routing—normally using the Border Gateway Protocol, or BGP—selects a path toward one of those locations. A user in one region may reach one server, while a user elsewhere reaches another, even though both send their DNS queries to the same IP address.
The selected node is commonly described as the “nearest,” but that means nearest according to routing policy and topology, not necessarily the shortest geographic distance. Peering relationships, route preferences, congestion, and network changes can all influence the path.
Anycast can be used for authoritative DNS, recursive DNS, content delivery, and other widely distributed services. For background on the different role of a resolver, see Recursive DNS server explained.
How an Anycast DNS query is routed
- A client or recursive resolver sends a DNS query to the service’s published IP address.
- Routers evaluate the available BGP paths for that address.
- The query follows the preferred path to one of the Anycast locations.
- The selected DNS server returns an answer using the same service address.
The application does not need to choose a city or maintain a list of server addresses. Routing makes that decision. If an operator withdraws the route for an unhealthy location, subsequent traffic can move toward another location that still advertises the address.
Why Anycast works well for DNS
DNS transactions are usually short. A query is sent, an answer returns, and the exchange ends quickly. That pattern fits Anycast better than a long-lived stateful session that could be disrupted by a route change halfway through the connection.
Modern DNS also uses TCP in several situations, including larger responses, retries, zone operations, and encrypted DNS transports. Providers therefore have to design their network and server state carefully rather than assuming that every request is a single stateless UDP packet.
Main benefits of Anycast DNS
Lower network latency
Queries can reach a well-connected regional node instead of crossing the Internet to a single origin. A shorter or better network path can reduce round-trip time, especially for a service with a broad user base.
Resilience against a location failure
When a node or network location becomes unavailable, its route can be withdrawn so traffic moves to another site. This avoids depending on one data center, but only when health detection and route control work correctly.
Distributed query capacity
Traffic is spread across multiple locations rather than concentrated on one server cluster. This provides more aggregate capacity and can help absorb regional traffic spikes.
A smaller attack concentration
Distributed nodes can prevent all malicious traffic from converging on one location. However, Anycast is not automatically complete DDoS protection. Capacity, filtering, rate controls, upstream cooperation, and incident response remain essential.
Anycast DNS and traditional redundancy
Anycast and secondary DNS solve related but different problems. Anycast makes one service address reachable from several routing locations. Secondary DNS gives a zone additional authoritative servers that can answer independently and receive zone data from a primary system.
A strong architecture can use both. For example, each authoritative provider may operate its own Anycast network, while the domain delegates to independent nameserver sets. The concepts in Backup DNS: Everything you need to know help explain why logical provider redundancy still matters.
What Anycast DNS does not guarantee
- It does not guarantee the geographically closest server. BGP selects routes according to network policy and reachability.
- It does not fix incorrect zone data. Every node can quickly return the same wrong answer if the underlying configuration is wrong.
- It does not replace DNSSEC. Anycast improves distribution and reachability; DNSSEC authenticates DNS data.
- It does not remove the need for monitoring. Operators must observe routing, node health, answer consistency, latency, and capacity.
- It does not eliminate every outage. Shared software, control-plane, configuration, or provider failures can affect multiple nodes at once.
Operational requirements behind a reliable service
Consistent DNS data
Every active node must serve the intended zone version. Providers need dependable distribution, validation, and rollback procedures so a partial update does not create different answers in different regions.
Accurate health checks
A server can be reachable while returning incorrect answers. Health checks should test the DNS service itself and validate important responses, not only confirm that a machine responds to a network probe.
Controlled route withdrawal
Failover depends on detecting a real problem and withdrawing the affected route without causing unnecessary instability. Operators should test this process and understand how quickly routing changes are accepted by neighboring networks.
Capacity in every failure scenario
The remaining nodes must handle redirected traffic when one or more sites are unavailable. Normal average load is not enough for capacity planning.
Global monitoring
Testing from multiple networks helps reveal regional routing problems that a monitor near the provider may not see. Useful measurements include DNS response correctness, latency, packet loss, route visibility, and the location serving each probe.
How to evaluate an Anycast DNS provider
When comparing services, look beyond the number of advertised locations. Ask how those locations connect to other networks, how traffic is shifted during failure, and how the provider verifies consistent answers. The existing list of DNS hosting providers provides a starting point, while the following questions help with deeper evaluation:
- Where are the active Anycast points of presence, and how are they connected?
- Does the provider publish uptime and incident information?
- How are unhealthy routes withdrawn, and are DNS answers tested before withdrawal?
- Are DNSSEC, access controls, change logs, monitoring, and DDoS defenses available?
- Can the service handle traffic when several locations fail simultaneously?
- Is independent secondary DNS supported for provider-level diversity?
Conclusion
Anycast DNS uses routing to make the same service address available from multiple network locations. It can reduce latency, distribute query load, and allow traffic to move away from an unhealthy site. Those benefits depend on sound BGP operations, synchronized zone data, application-level health checks, sufficient spare capacity, and monitoring from many regions.
For another practical overview, see What is Anycast DNS and how does it work?. The operational behavior and design considerations for Anycast services are documented in RFC 4786: Operation of Anycast Services.
List of DNS hosting providers to choose from
When searching for the best DNS hosting providers for your needs, you must consider the reputation, quality of service, advanced DNS features, limits of resources, security, and price. It could be a very hard decision. This is why we have created a short list that could help you with the initial research.