How to Setup DNS
DNS Blog
DNS over TLS Explained: How DoT Protects Resolver Traffic
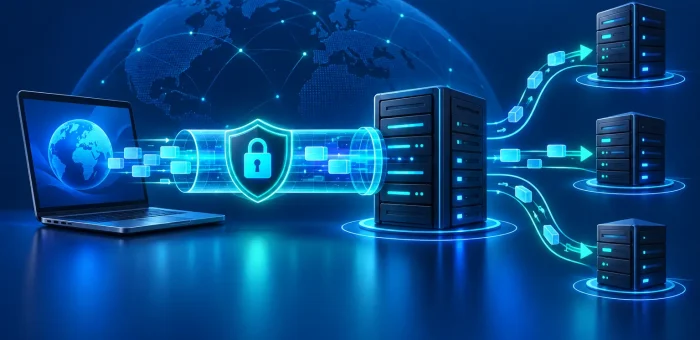
Traditional DNS queries are commonly sent without encryption. Anyone able to observe the path between a device and its recursive resolver may be able to see the names being requested, and an active attacker on that path may try to interfere with the exchange. DNS over TLS, usually shortened to DoT, protects this part of resolution by carrying DNS messages through an encrypted TLS connection.
DoT improves confidentiality and integrity between the client and the selected resolver. It does not hide every network destination, make the user anonymous, or automatically protect communication beyond the resolver. Understanding that boundary is essential when deciding where and how to deploy it.
How DNS over TLS works
A device first establishes a TCP connection to a DoT-capable recursive resolver, conventionally on port 853. It then performs a TLS handshake, validates the resolver’s identity according to the configured authentication policy, and sends ordinary DNS messages inside the encrypted connection.
The DNS questions and answers retain their normal wire format. TLS changes the transport channel rather than the records themselves. Connections can be reused for multiple queries, which avoids repeating the full setup for every lookup and reduces overhead.
The recursive resolver still performs the rest of the lookup process: it uses cached data when available or queries root, top-level-domain, and authoritative servers. The existing article Recursive DNS server explained describes that role in more detail.
DoT compared with traditional DNS
Conventional DNS commonly uses UDP on port 53 and switches to TCP when required. Those transports do not provide encryption or server authentication by themselves. DoT places DNS inside TLS, adding confidentiality, integrity protection, and the ability to authenticate the resolver endpoint.
Encryption prevents a local observer from directly reading the DNS payload between client and resolver. It also makes undetected modification of that protected exchange much harder. However, an observer may still infer activity from destination IP addresses, connection timing, traffic volume, and other metadata.
DoT compared with DNS over HTTPS
DNS over HTTPS, or DoH, also encrypts DNS messages with TLS, but it carries them through HTTPS and normally uses port 443. DoT uses a dedicated DNS-over-TLS service, conventionally on port 853. A practical comparison is available in the ClouDNS guide to DoT and DoH, placed here in the first half of the article.
The dedicated port makes DoT easier for network administrators to identify, permit, redirect, or block. DoH can blend with ordinary HTTPS traffic and is frequently configured inside a browser or application. That can be useful on restrictive networks but may bypass local DNS policy, internal zones, or organization-approved filtering.
Neither protocol is universally superior. A managed network may prefer system-level DoT for clear policy control, while a browser or application may use DoH for portability. The important questions are who selects the resolver, how its identity is authenticated, what happens when encryption fails, and whether all applications follow the same policy.
Privacy and security benefits
Protection on untrusted local networks
On public Wi-Fi or another network you do not control, plaintext DNS can expose query names to nearby or on-path observers. DoT encrypts the DNS exchange from the device to the configured resolver, reducing this local visibility.
Integrity of the client-to-resolver channel
TLS detects modification of protected messages and authenticates the server when certificate verification and resolver naming are configured correctly. This helps prevent a network attacker from silently replacing DNS answers on that segment.
Consistent resolver choice
A device configured with a known DoT resolver can use the same service across multiple networks rather than automatically accepting the DNS server advertised by each local router. This creates a clearer trust relationship, although it also makes the selected resolver an important dependency.
The limits of DNS over TLS
DoT protects only the connection between the client and recursive resolver. The resolver sees the questions it must process and may associate them with connection metadata. Resolver selection therefore matters. Review the operator’s logging, retention, filtering, jurisdiction, security, and availability policies.
Communication from the recursive resolver to authoritative DNS servers is not automatically encrypted merely because the client used DoT. The resolver may use ordinary DNS upstream unless the architecture explicitly supports additional protected transports.
DoT also does not conceal the IP address contacted after resolution, secure an unsafe website, replace HTTPS, block malware by itself, or guarantee anonymity. It is one privacy and transport-security control within a larger system.
DoT and DNSSEC solve different problems
DoT encrypts and authenticates a transport channel to a resolver. DNSSEC allows a validating resolver to verify signatures on DNS data and build a chain of trust from the root. A resolver can use both: DoT protects the client connection, while DNSSEC validation checks the authenticity and integrity of signed records.
The article DNSSEC explained covers that separate security model. Neither mechanism repairs an incorrect record; authenticated incorrect data remains incorrect.
Strict authentication and fallback behavior
Encryption without reliable endpoint authentication may connect the client securely to the wrong resolver. A strong deployment knows the intended resolver identity and validates its certificate. The client should also have a defined policy for connection failure.
A strict policy refuses to send the query in plaintext when the authenticated DoT service is unavailable. This preserves privacy but can interrupt DNS resolution during an outage or blocked connection. An opportunistic policy may fall back to ordinary DNS, improving reachability but allowing a network to force a downgrade and observe queries.
The appropriate choice depends on the environment and risk model. Whichever behavior is chosen should be visible, documented, and monitored rather than silently assumed.
Where DoT can be configured
Operating system
System-level configuration can protect queries from multiple applications and give administrators a consistent policy. Implementation details vary, and applications that use their own resolver libraries may bypass the system setting.
Router or gateway
A local gateway can accept DNS from client devices and forward it to an external resolver over TLS. This protects the gateway-to-resolver segment, but client-to-gateway queries may remain unencrypted unless the local network uses an encrypted mechanism as well.
Local forwarding resolver
A managed forwarding service on the device or network can provide caching, policy, and DoT upstream. Administrators must secure the local listener and ensure that firewall rules do not expose an unintended open resolver.
Testing a DNS over TLS deployment
Begin with ordinary lookups to establish expected answers. The site’s DNS lookup guide explains common tools, but note that a standard dig query does not prove the operating system used DoT.
Verify the deployment at several layers:
- Confirm resolver identity. Check the configured endpoint name and successful certificate validation.
- Verify the transport. Use client logs, resolver logs, packet capture, or platform diagnostics to confirm TLS on the expected connection.
- Test normal records. Resolve A, AAAA, MX, and other types used by applications.
- Test DNSSEC behavior. Confirm that valid signed domains resolve and known validation failures are handled as expected.
- Test failure policy. Block or stop the DoT endpoint temporarily in a controlled environment and observe whether the client fails closed or falls back.
- Check internal names. Ensure corporate, VPN, split-horizon, and local-service names continue to resolve under the selected policy.
- Measure performance. Compare connection setup, reused-connection latency, cache behavior, and failure recovery.
Operational considerations
Port 853 must be reachable through relevant firewalls and captive networks. The resolver needs valid certificates, capacity for TLS connections, connection reuse, monitoring, and protection against resource exhaustion. Clients need accurate time for certificate validation and a trusted certificate store.
High availability is important because an enforced encrypted resolver becomes a critical dependency. Configure supported backup endpoints carefully and make sure failover does not silently select a resolver with a different privacy or filtering policy.
The protocol requirements and message framing for DNS over TLS are defined in RFC 7858: Specification for DNS over Transport Layer Security.
Conclusion
DNS over TLS protects DNS messages between a client and recursive resolver with an authenticated encrypted connection. Its dedicated transport is well suited to system and network policy, but the privacy benefit depends on correct certificate validation, a trustworthy resolver, explicit fallback behavior, and reliable operations. Use DoT alongside HTTPS, DNSSEC validation, secure endpoints, and clear monitoring rather than treating it as a complete privacy solution.
DNSSEC explained
DNSSEC can be spotted as an application to, in other cases, insecure DNS. It brings cryptography within and a complete line of trust. That is a guarantee for each level and implements top-notch security for your domain.
What is DNSSEC?
The short DNSSEC is an acronym for Domain Name System Security Extensions. The primary DNS is reliable and fast, but its downside is that it lacks security. Back in the days when it was created, it wasn’t that of a problem. Later on, things change.